Project under NDA
A cybersecurity company website with no attack surface
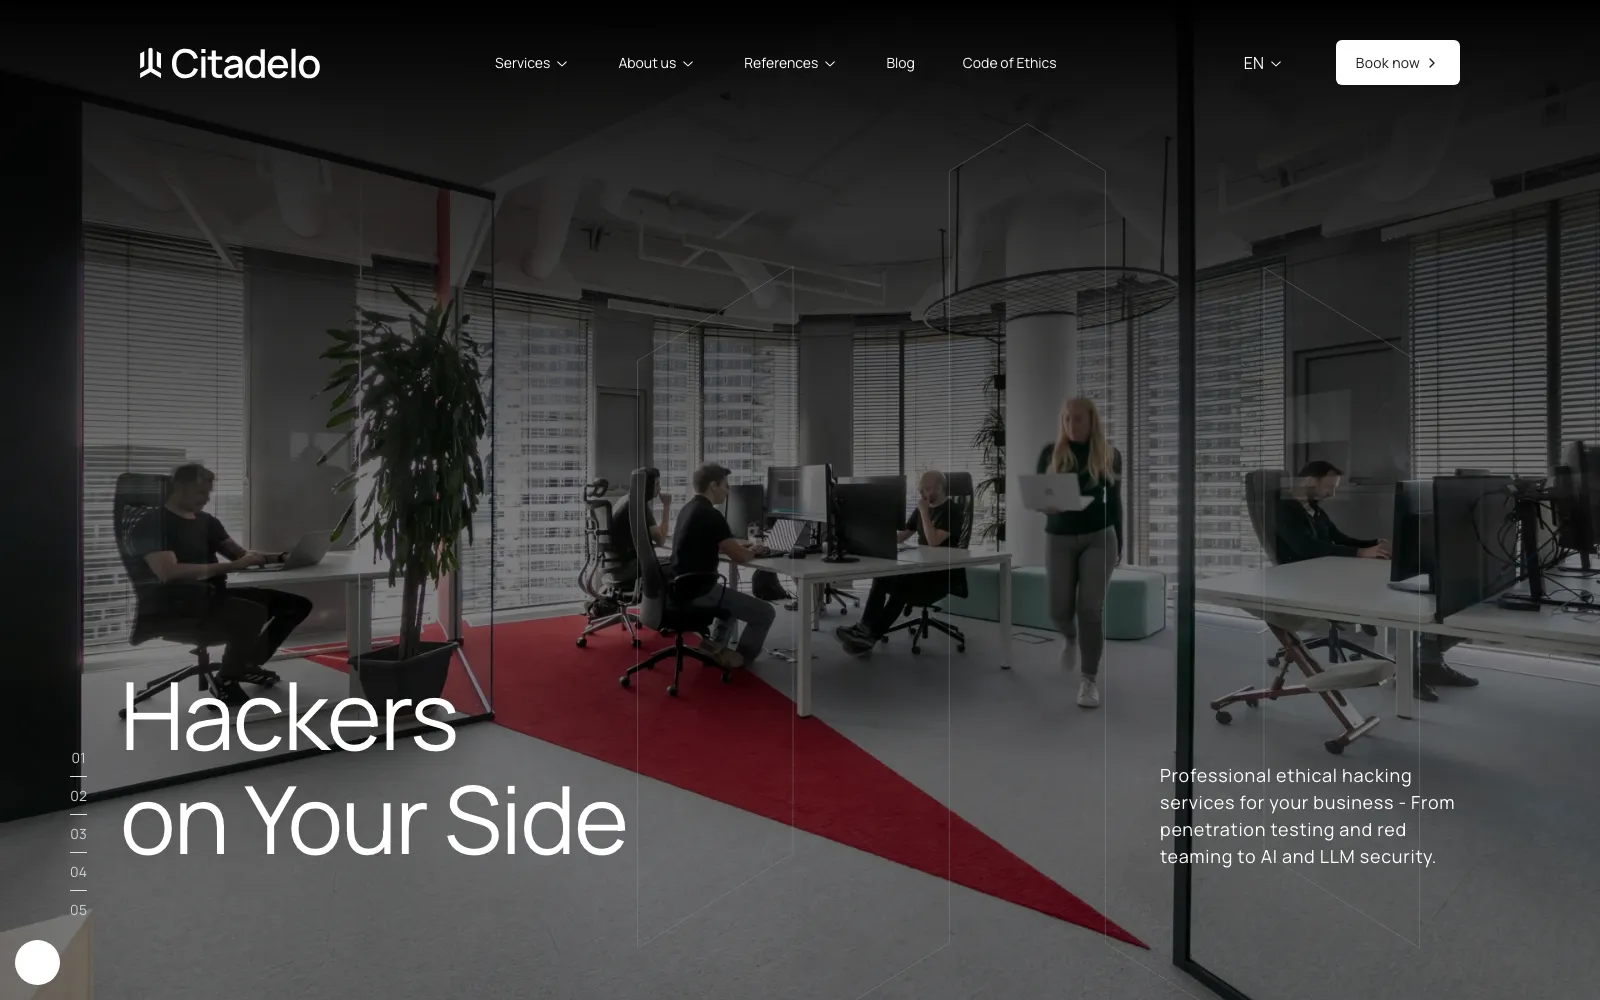
Website of a cybersecurity company built as a secure static deployment with Next.js, Strapi, GitLab CI/CD and Cloudflare Pages, while keeping content editing simple.
Results
- 0
- servers exposed in production
- CMS
- content editing without touching code
- CI/CD
- automatic publishing on every change
The challenge
The client does penetration testing and security audits. Its own website could not carry the usual vulnerabilities of a CMS exposed to the internet, but the marketing team needed to keep editing content without a developer.
What we built
A headless CMS and static deployment architecture: Strapi as the content editor in a private environment, Next.js to generate the site, and a GitLab CI/CD pipeline that publishes the output to Cloudflare Pages on every change. In production there is no reachable application server or database.
Outcome
Server-side vulnerabilities disappear from the public site, and the editing flow stays that of a normal CMS.
Related cases
Project under NDA
Pub-quiz platform: Laravel migration and a quiz shop
Migration of the core application of the leading Czech pub-quiz organiser from Nette to Laravel, cloud deployment and a new e-commerce module with GoPay.
PHPLaravelLivewire
Shall we talk about your project?
Tell us what you need. We reply within one business day with a concrete proposal.